What is External Attack Surface Management (EASM)?
EASM continuously discovers and monitors internet-facing assets to find exposures attackers use for initial access. See how it works, its scope, and metrics.
External attack surface management (EASM) is the continuous discovery, monitoring, and analysis of an organization's internet-facing assets to find exposures attackers use for initial access.
The work happens from outside the network, using the same public data sources and scanning methods an attacker uses.
Internal inventories record what teams deployed on purpose and remembered to document. EASM records what is actually reachable from the internet, which includes forgotten subdomains, staging servers, cloud storage opened during a migration, and assets inherited through acquisitions.
Constant change drives the discipline more than any single threat. External environments shift with every deployment, DNS record, and vendor integration, so EASM runs as continuous monitoring instead of a periodic audit.
What Counts as the External Attack Surface
The external attack surface covers every asset an outsider reaches without credentials or internal access.
Domains and DNS records: Registered domains, subdomains, MX and TXT records, and the dangling entries behind a subdomain takeover.
IP ranges and network services: Owned and leased address space, open ports, remote access gateways, and management interfaces left reachable.
Web applications and portals: Customer sites, admin consoles, staging environments, legacy applications, and login pages nobody decommissioned.
APIs: Public and partner endpoints, undocumented versions, and development instances covered by API security controls only where teams knew they existed.
Mobile applications: Published apps and the hardcoded secrets, endpoints, and cloud buckets inside them.
Cloud assets: Storage buckets, serverless endpoints, container registries, and workloads spun up outside central cloud security review.
Certificates and email infrastructure: Expiring or weak TLS certificates, and SPF, DKIM, and DMARC records that permit spoofing.
Exposed code and secrets: Public repositories, paste sites, and build artifacts holding credentials or leaked API keys.
Third-party hosted assets: Marketing sites, vendor portals, and SaaS tenants carrying the organization's brand and data.
AI-facing assets: Model endpoints, inference APIs, and shadow AI services connected to corporate data.
How External Attack Surface Management Works
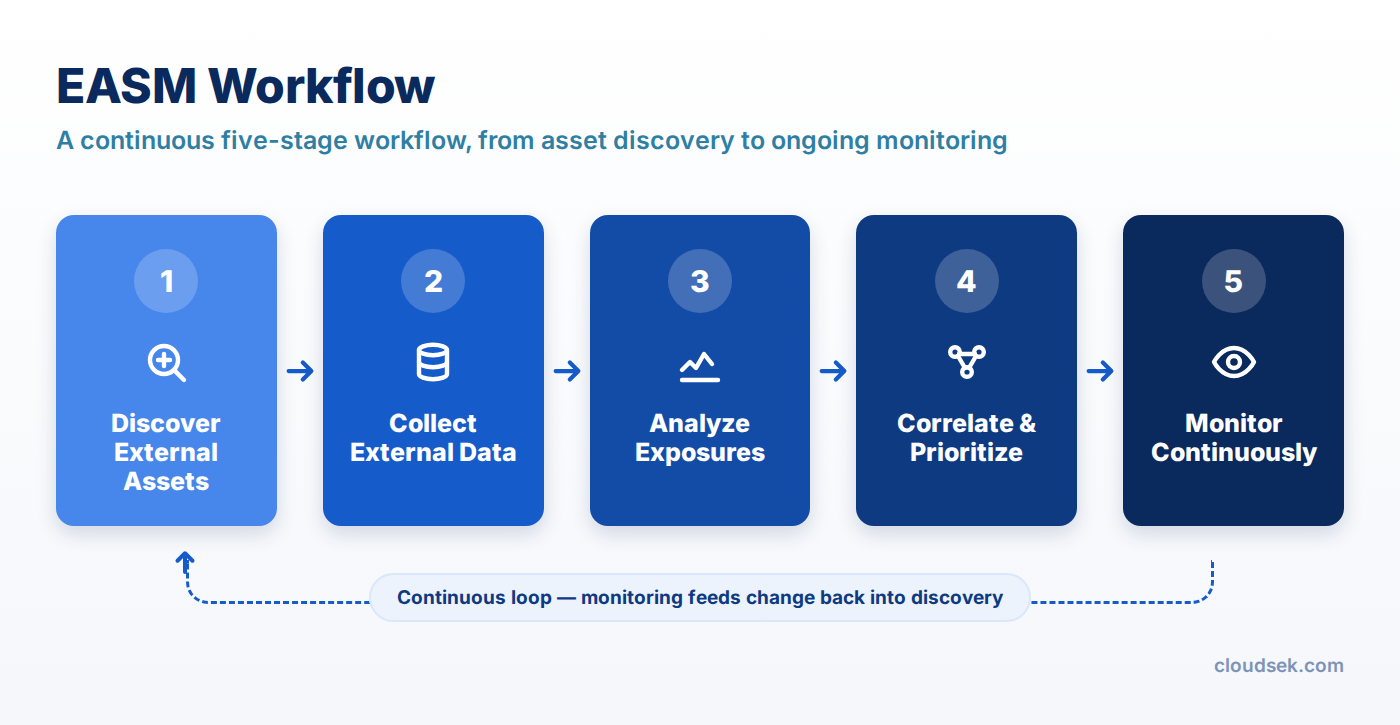
EASM works by attributing assets to the organization, collecting external evidence about each one, analyzing exposures, prioritizing findings, and repeating the cycle continuously.
Seed and attribute: Start from known domains, brands, IP ranges, and ASNs, then expand through registrant data, DNS relationships, and certificate records to assets nobody registered centrally.
Collect external data: Gather DNS records, certificate transparency logs, internet-wide scan results, WHOIS data, mobile app store listings, and public code repositories.
Analyze exposures: Check each asset for known CVEs, weak TLS settings, DNS misconfigurations, exposed admin panels, directory listings, default credentials, and leaked secrets.
Correlate and prioritize: Connect related findings across assets, weigh exploitability and business importance, and rank what opens a path toward a critical system.
Monitor and reassess: Re-scan on a defined cadence so new deployments, expired certificates, and newly disclosed vulnerabilities surface as they appear.
Discovery Techniques Behind EASM
Discovery quality separates a useful EASM program from an incomplete asset list.
Passive DNS and reverse lookups: Historical resolution data reveals subdomains and hosts absent from current records.
Certificate transparency logs: Every public certificate issued names the hosts it covers, including internal-sounding staging systems.
ASN and IP allocation records: Registry data maps network blocks back to the organization and its subsidiaries.
Internet-wide scan data: Banner and service data identify software versions, exposed protocols, and management interfaces.
Favicon and content fingerprinting: Shared icons, page hashes, and analytics identifiers link unattributed hosts to known properties.
Source and artifact analysis: Mobile app binaries, public repositories, and JavaScript bundles expose internal endpoints and hardcoded credentials.
Why External Attack Surface Management Matters
Attackers scan the same internet that defenders sample occasionally, and exploitation of exposed systems remains a leading route into organizations.
ENISA's Threat Landscape 2025, built on roughly 4,875 curated incidents, found vulnerability exploitation behind 21.3% of intrusions, with campaigns weaponizing flaws in VPN appliances, collaboration platforms, and mail servers within days of disclosure.
Mandiant's M-Trends 2026 puts exploitation first among initial infection vectors for the sixth consecutive year, at 32% of intrusions. Gartner, in the research that introduced continuous threat exposure management, projected a threefold reduction in breach likelihood by 2026 for organizations that prioritize security investments through such a program.
Regulators now treat asset discovery as a baseline control, with a stated cadence. CISA's Binding Operational Directive 23-01 requires federal civilian agencies to run automated asset discovery every 7 days and vulnerability enumeration every 14 days, a cadence private organizations use as a benchmark.
Closes visibility gaps: Finds known, unknown, and unmanaged assets across domains, cloud services, and shadow IT.
Removes initial access vectors: Identifies misconfigurations and vulnerabilities before they become entry points for a zero-day or N-day exploit.
Covers third-party exposure: Surfaces vendor-hosted assets and integrations that sit outside internal controls, complementing vendor risk monitoring.
Shortens exposure windows: Detects newly exposed assets in days instead of at the next audit cycle.
Unifies external evidence: Brings DNS, certificate, scanning, and intelligence data into one view analysts act on.
What EASM Finds in Practice
Outside-in scanning surfaces the ordinary mistakes that cause real breaches, not exotic vulnerabilities.
CloudSEK's BeVigil scanner found a high-profile asset with directory listings left enabled, exposing authentication tokens, personal data, and database logs to anyone who requested the URL. No exploit was required, since the web server offered the contents on request.
Third-party assets produce the same pattern under a different owner. In one CloudSEK case study, a misconfigured .git directory on a vendor-hosted application exposed backend source code and AWS credentials belonging to a major bank, which handed attackers a route into cloud infrastructure through a third-party breach.
Recurring findings across programs follow a short list: expired or weak certificates, exposed database and admin ports, forgotten staging environments, dangling DNS records, unpatched edge appliances, and secrets committed to public repositories.
When Organizations Use EASM
EASM earns its place at specific moments, and each one produces a different question for the program to answer.
Mergers and acquisitions: Discovery maps an acquired company's external footprint before its networks connect to the parent organization.
Cloud migration: Continuous scanning catches storage, endpoints, and management interfaces exposed during a move between environments.
Shadow IT discovery: Assets registered on corporate cards or personal accounts appear in DNS and certificate data even when no ticket exists.
Subsidiary oversight: Group security teams gain visibility into regional entities that run their own infrastructure and vendors.
Emerging vulnerability response: When a flaw in an edge appliance is disclosed, the external inventory answers whether the organization runs it, and where.
Pre-incident and post-incident review: Analysts check which exposures existed at the time of an intrusion, including those used by an advanced persistent threat group.
Audit and compliance evidence: Continuous inventories support control requirements that ask organizations to know and monitor their internet-facing assets.
EASM vs ASM, CAASM, DRPS, and CTEM
These disciplines overlap in marketing and differ in scope, data source, and the question each one answers.
Discipline
Scope
Primary Data Source
Question It Answers
EASM
Internet-facing assets and their exposures
External scanning and public data
What can an attacker see and reach?
ASM
Internal and external attack surface
Mixed internal and external sources
Where is the organization exposed overall?
CAASM
All known cyber assets, inside out
APIs of EDR, CMDB, cloud, and scanners
What assets exist and how are they covered?
Vulnerability Management
Known assets under management
Authenticated and network scanners
Which flaws on known assets need patching?
DRPS
Brand, data, and identity exposure
Dark web, paste sites, social platforms
Where is the organization exposed beyond infrastructure?
CTEM
Program covering all exposure types
Output of the disciplines above
Which exposures deserve investment first?
Sequence matters more than the boundaries between these categories. EASM discovers what exists, vulnerability management fixes what is known, DRPS covers exposure that no scanner detects, and CTEM organizes the whole effort into a repeatable cycle.
Benefits of an EASM Program
Faster response to new exposure: Continuous detection shortens the gap between an asset appearing and a team acting on it.
Less manual effort: Consolidated external data replaces spreadsheet reconciliation across DNS, certificate, and scanning sources.
Change tracking: Acquisitions, migrations, and vendor integrations show up as measurable shifts in external exposure.
Progress measurement: Exposure trends give security leaders evidence that remediation is working, feeding governance under an information security management system.
Better prioritization: Attacker-visible context helps teams rank findings by reachability instead of raw severity scores.
Coordinated remediation: A single external inventory gives infrastructure, application, and vendor teams one list to work from.
Common Challenges in EASM Programs
Attribution errors: Discovery claims assets the organization does not own, or misses assets registered under subsidiaries and partner accounts.
False positives: Banner-based detection flags versions that are patched or services that are already restricted, which erodes trust in the tool.
Ownership gaps: A discovered exposure stalls when nobody knows which team runs the asset.
Scale and churn: Large environments generate thousands of assets and constant change, which buries meaningful findings in volume.
Missing business context: Exploitability and asset importance decide urgency, and neither appears in the scan result itself.
Discovery without capacity: Finding more exposure than the remediation pipeline absorbs turns the program into a backlog generator.
Validation addresses most of these problems at once. Confirming a finding against the live asset, then routing it with an owner and a deadline, converts discovery into remediation that a SOC can track.
EASM Metrics Worth Tracking
Useful EASM metrics measure coverage, speed, and whether exposure is shrinking.
Unknown asset ratio: Share of discovered assets missing from the official inventory, which shows how wide the visibility gap runs.
Time to discovery: Days between an asset appearing online and the program detecting it.
Time to remediation by severity: How long critical exposures stay open once assigned.
Recurring exposure classes: Which misconfiguration types keep returning, pointing to a process or template problem.
Assets with a named owner: Percentage of external assets mapped to an accountable team.
Exposure aging: Count of findings open beyond their target window, tracked alongside security monitoring metrics.
External Attack Surface Management (EASM) Best Practices
Define scope by seeds, not guesses, listing every brand, domain, subsidiary, and acquired entity that discovery starts from.
Set a discovery cadence and hold to it, using the weekly discovery and fortnightly enumeration pattern in CISA's directive as a reference point.
Assign asset ownership before findings arrive, so remediation routes automatically instead of stalling in triage.
Baseline normal exposure and alert on deviation, such as a new open port or an unexpected certificate.
Validate before escalating, confirming exploitability so engineering teams trust the queue.
Integrate with ticketing and SIEM, turning findings into tracked work items rather than dashboard entries.
Review third-party assets on a schedule, including vendor-hosted subdomains and partner integrations tied to supply chain risk.
Retire what nobody needs, since removing an exposed asset closes the risk permanently and patching only defers it.
The UK NCSC's asset management guidance makes the same point for the discipline as a whole: asset information stays useful only when it is maintained continuously and integrated with the teams that act on it.
How CloudSEK BeVigil Operationalizes EASM
CloudSEK built BeVigil as its external attack surface monitoring platform. It fingerprints internet-facing infrastructure from the public internet, so the inventory reflects what an attacker enumerates rather than what a CMDB records.
Scanning runs across eight surfaces, and each maps to a category of initial access vector: web applications, mobile applications, APIs, cloud, CVE, DNS, SSL, and network. Findings include exposed admin interfaces, hardcoded secrets, misconfigured storage, subdomain takeovers, missing SPF and DMARC records, weak ciphers, and open ports.
Continuous re-scanning catches exposures introduced by new deployments and shadow IT, while more than 600 tag classifiers narrow results to the findings that open a real path. Those findings then feed CloudSEK's attack path correlation, which shows which exposure to close first.
EASM FAQs
Is EASM the same as penetration testing?
No. Penetration testing validates exploitability at a point in time, while EASM continuously discovers and monitors exposed assets across the whole external footprint.
Does EASM require agents or credentials?
No. EASM operates from outside using public data and unauthenticated scanning, so it finds assets no internal system records.
Can EASM cover subsidiaries and acquisitions?
Yes, once their domains, brands, and network ranges are added as discovery seeds. Acquisitions are a common source of unknown external assets.
How does EASM relate to dark web monitoring?
EASM covers exposed infrastructure. Dark web monitoring covers leaked data, credentials, and attacker chatter, and mature programs run both.
Who owns EASM in an organization?
Most organizations run it through security operations or vulnerability management teams, with infrastructure, application, and cloud teams remediating the assets they operate.
Is EASM only for large organizations?
No. Smaller teams gain the most, since they lack the headcount for manual external audits and still run internet-facing infrastructure.
Vendor risk includes cybersecurity, operational, compliance, financial, reputational, strategic, fourth-party, geopolitical, and AI-related risks. See what to monitor.