What are Attack Graphs? Components, How They Work, and Use Cases

An attack graph maps how an attacker moves through a network to reach critical assets. Learn the components, types, use cases, and how attack graphs work.
Published on
Monday, September 21, 2026
Updated on
September 20, 2026

An attack graph is a graphical model of the routes an attacker could take through an environment to reach a target. Nodes represent systems, conditions, or vulnerabilities, and edges represent the exploits or actions that move an attacker from one state to the next. The graph turns a list of separate weaknesses into a connected map of how those weaknesses chain together.

Attack graphs answer a question that vulnerability scans cannot. A scan reports shows which flaws exist, while an attack graph shows which flaws sit on a path to something that matters. That distinction lets teams focus on the exposures that actually lead to a breach.

This guide explains what attack graphs are, the components that make them up, and how they work. It covers attack graphs versus attack trees and attack paths, the main types, how to build one, the benefits, use cases, best practices, and the limitations to plan around.

What are Attack Graphs?

Attack graphs provide context for understanding how individual security conditions can combine to create a viable attack scenario, showing how vulnerabilities, compromised assets, credentials, and privileges can influence subsequent attacker actions. 

The shift toward this approach is well documented. Gartner introduced continuous threat exposure management in 2022 and predicts that organizations prioritizing it will be three times less likely to suffer a breach by 2026. Attack graphs sit at the center of that shift, turning isolated vulnerability lists into the connected attack paths an attacker would actually follow.

Four traits define an attack graph:

  • Path-modeling: it maps multi-step routes, not single flaws.
  • Relationship-aware: it shows how systems and exposures connect.
  • Predictive: it anticipates attacker movement before an attack.
  • Prioritization-enabling: it ranks exposures by their place on a path.

Why Attack Graphs Matter

Attack graphs give security teams a connected view of how weaknesses interact across an environment. Instead of looking at security findings individually, teams can understand relationships between assets, access conditions, attacker actions, and security controls.

  • Connect security findings: Bring information from vulnerabilities, configurations, privileges, and assets into a single model.
  • Provide context: Show how the condition of one system can affect the security of another connected system.
  • Reduce security noise: Help teams distinguish meaningful relationships from isolated findings that have limited impact.
  • Support security validation: Provide a model that can be compared against real-world testing to check whether assumed attack scenarios are feasible.
  • Improve security communication: Turn complex technical relationships into a visual model that security teams and decision-makers can understand more easily.
  • Adapt to changing environments: When assets, configurations, or vulnerabilities change, the graph can be updated to reflect the current environment.

Components of an Attack Graph

An attack graph is built from five components:

Component What it Represents
Nodes Systems, conditions, privileges, or vulnerabilities in the environment.
Edges The exploits or actions that move an attacker between nodes.
State Information The current status of each node, such as open ports, running services, or whether it is compromised.
Attack Actions The specific techniques used to exploit a node, such as privilege escalation or lateral movement.
Constraints The preconditions that must hold for an action to succeed, such as an open port or valid credentials.

These components combine into a working model: nodes and edges form the structure, while state information, attack actions, and constraints make the paths realistic rather than theoretical.

How Attack Graphs Work

An attack graph models how an attacker could move from an initial entry point to a target by connecting assets, vulnerabilities, and attacker actions. It shows how separate exposures can form a sequence of steps within the environment. The result shows not just where weaknesses exist, but which ones an attacker would actually use.

An attack graph performs four functions:

  • Identify entry points: it maps where an attacker could first gain access.
  • Attack actions: The exploits, credentials, or techniques used to move forward.
  • Connected paths: How an attacker could move between systems or privileges.
  • Target assets: The critical systems or data an attacker is trying to reach.
sample attack graph

A sample attack graph: two entry paths converge at a choke point before reaching the critical asset.

Points where many paths converge are choke points. A single fix at a choke point can break multiple attack paths at once, which makes choke points the highest-value place to focus defense.

A worked example shows the pattern. An attacker exploits an exposed web server to gain a foothold, then moves to a workstation through a phishing payload and to a file server through a shared credential. Both routes converge on a domain admin account, which unlocks the critical database. The graph reveals that securing the domain admin account, the choke point, breaks both paths before the attacker reaches the data.

Attack Graph vs Attack Tree vs Attack Path

Attack graphs, attack trees, and attack paths are related but distinct. An attack graph models many interconnected routes across an environment. An attack tree breaks a single attacker goal into a hierarchy of sub-goals and steps. An attack path is one route through the graph, from entry to target.

attack graph vs tree vs path

An attack graph maps many converging routes, an attack tree breaks one goal into a hierarchy, and an attack path is a single route through the graph.

Aspect Attack Graph Attack Tree Attack Path
Structure Interconnected nodes and edges. Hierarchical, goal at the root. A single chain of steps.
Scope A whole network. One attacker goal. One route to one target.
Best Use Mapping real enterprise networks. High-level threat modeling. Describing or testing one scenario.

In practice, teams use attack trees to reason about a single goal, attack graphs to map a whole environment, and attack paths to describe or test the specific routes the graph reveals.

Types of Attack Graphs

Attack graphs fall into a few common types, grouped by what their nodes represent and how they are produced:

  • State-based graphs: nodes represent network states, and edges represent exploits that move the network into a more compromised state.
  • Condition or dependency graphs: nodes represent the pre-conditions and post-conditions of an exploit, and edges represent the dependencies between them.
  • Manual graphs: drawn by hand by red teams, accurate but slow and hard to scale.
  • Automated graphs: generated by tooling that ingests scan and configuration data, scaling to large and changing networks.

Most enterprise programs now favor automated, continuously updated graphs over static ones, because networks change faster than a manual graph can track.

How to Build an Attack Graph

Building an attack graph follows five steps:
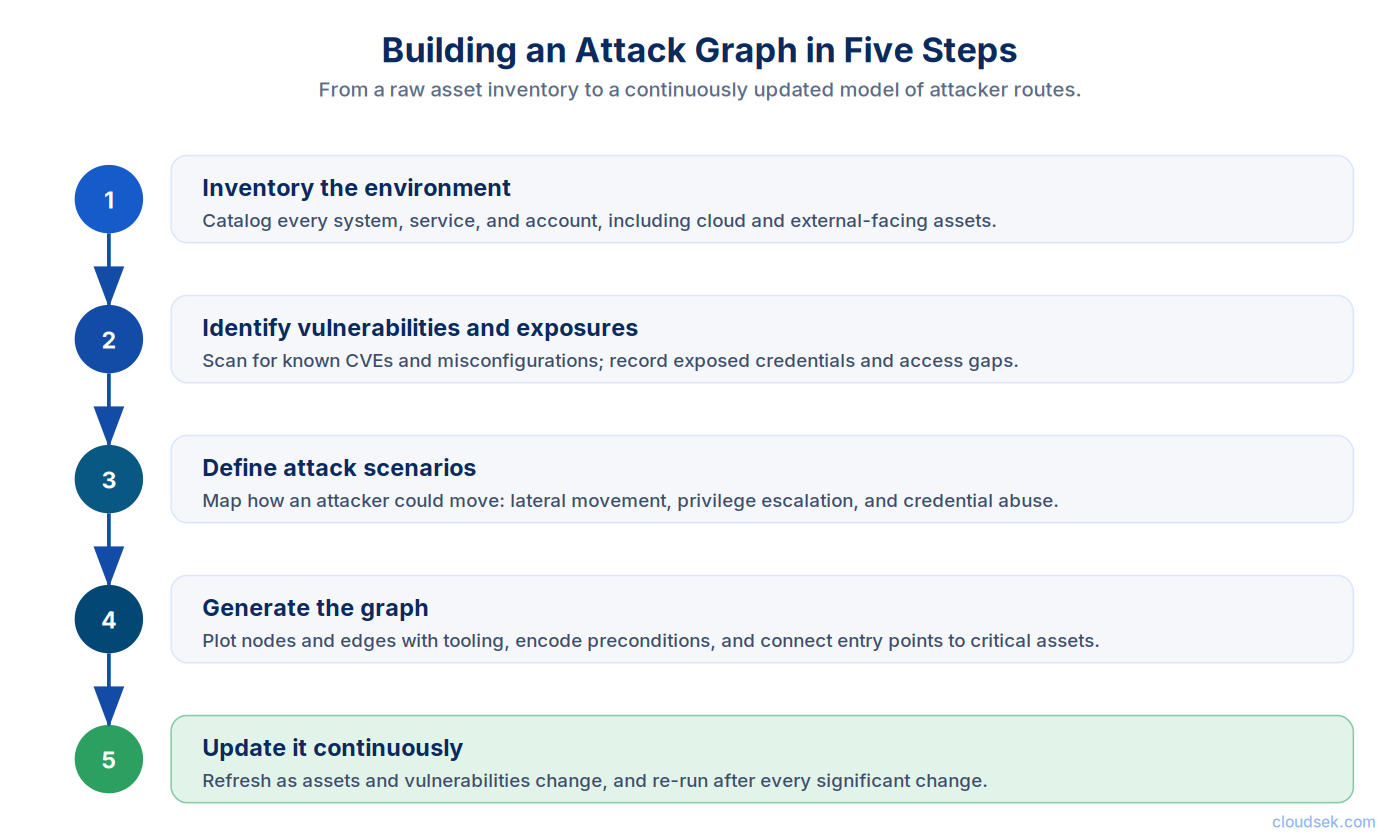
how to build an attack graph
  1. Inventory the environment. First, catalog every asset that could appear on a path.
  • List systems, services, and accounts.
  • Include cloud and external-facing assets.
  1. Identify vulnerabilities and exposures. Second, find the weaknesses attackers could use.
  • Scan for known CVEs and misconfigurations.
  • Record exposed credentials and access gaps.
  1. Define attack scenarios. Third, map how an attacker could move from each entry point.
  • Include lateral movement and privilege escalation.
  • Consider phishing, exploitation, and credential abuse.
  1. Generate the graph. Fourth, plot the nodes and edges with tooling.
  • Encode the preconditions each action requires.
  • Connect entry points to critical assets.
  1. Update it continuously. Fifth, keep the graph current as the environment changes.
  • Refresh as assets and vulnerabilities change.
  • Re-run after major configuration changes.

Use Cases of Attack Graphs

Attack graphs support four common use cases:

  • Penetration testing and red teaming: testers use graphs to plan realistic multi-step attacks, a practice red teams once did by hand. The graph surfaces paths a single-vulnerability test would miss.
  • Incident response: responders use graphs to trace how an attack could spread and decide what to contain first. The graph turns a live alert into a map of likely next moves.
  • Vulnerability and exposure prioritization: teams patch the flaws that sit on real attack paths first. The graph separates the few exposures that enable a breach from the many that do not.
  • Threat modeling: graphs map to MITRE ATT&CK techniques to connect exposures to known attacker behavior. The mapping shows whether current detection covers the techniques on each path.

Best Practices for Using Attack Graphs

Attack graphs remain useful when they reflect the current environment, include relevant security data, and are validated against real-world conditions. The following practices help security teams maintain accurate and actionable attack graphs:

  1. Integrate with Existing Security Tools: Connect attack graphs with tools such as SIEMs, vulnerability scanners, asset management platforms, and security monitoring systems. This allows the graph to use current security data and fit into existing workflows.
  2. Keep Graphs Updated: Regularly refresh asset, vulnerability, configuration, and access data as the environment changes. This helps prevent outdated information from creating inaccurate attack paths.
  3. Incorporate Threat Intelligence: Use current information about vulnerabilities, attacker techniques, and emerging threats to improve the relevance of modeled attack scenarios. Threat intelligence can help identify attack techniques that may affect the environment.
  4. Model Security Controls: Include controls such as network segmentation, authentication, access restrictions, and endpoint protection when building attack paths. This helps distinguish theoretical routes from paths that are feasible in the actual environment.
  5. Validate Attack Paths: Compare important paths against penetration tests, red team exercises, or other security validation activities. Testing helps identify inaccurate assumptions and keeps the graph aligned with the real environment.

Attack Graphs in Predictive Exposure Management

Attack graphs have moved from static diagrams to continuous, automated models. Modern programs generate them from live data and refresh them as the environment changes, which fits the continuous threat exposure management (CTEM) approach now standard in exposure programs.

The newest systems use AI to correlate signals from many sources into predictive attack graphs. Rather than mapping a network once, they continuously predict how an attacker would chain exposures into a path, so teams disrupt the path before execution rather than after a breach.

The CTEM framework runs in five stages: scoping, discovery, prioritization, validation, and mobilization. Attack graphs feed the prioritization and validation stages, showing which exposures sit on a real path and confirming whether existing controls break it.

How CloudSEK Nexus AI Builds Predictive Attack Graphs

CloudSEK Nexus AI is an attack path intelligence layer that correlates signals from across CloudSEK's platform into predictive attack graphs. It ingests digital risk and dark web exposure, threat actor and CVE intelligence, the external attack surface, the AI attack surface, and third-party risk, then maps how an attacker would chain those signals into a real, executable attack path.

Nexus AI builds its attack graph from external, AI, and third-party signals, focused on the initial access vector and how attackers get in, rather than mapping internal host-by-host movement. It scores each path by exploitability and attacker behavior, so security teams disrupt attack chains across the AI attack surface and beyond before they execute.

CloudSEK's research shows how a predictive attack graph forms in practice. In one published finding, AIVigil discovered an unauthenticated MCP server on a customer's AI attack surface. An attacker could enumerate its exposed tools and chain them into server-side request forgery, local file inclusion, and the theft of live AWS credentials. Nexus AI correlates that AI-layer entry point with related signals, such as a leaked credential or an exposed vendor, into a single attack graph that shows the full path to the data rather than three disconnected alerts.

Frequently Asked Questions

How do attack graphs support vulnerability management?

They show how vulnerabilities relate to assets and other exposures, providing context for remediation decisions.

What is the difference between an attack graph and a vulnerability scan?

A vulnerability scan identifies individual weaknesses, while an attack graph connects those weaknesses with assets, access conditions, and attacker actions to model how they could be used together.

How do security controls affect attack graphs?

Controls such as segmentation and access restrictions can block or alter potential routes represented in the graph.

Can attack graphs support incident investigation?

Yes. They can help security teams understand relationships between compromised systems, privileges, and potential attacker movement.

How do attack graphs fit into CTEM?

Attack graphs can support CTEM by connecting discovered exposures and helping security teams understand how they relate to potential attack scenarios. They can be particularly useful during exposure prioritization and validation.

Related Posts
12 Common Cyber Attack Vectors You Should Know
Cyber attack vectors include phishing, compromised credentials, exposed software, API abuse, supply chain threats, and other paths attackers use for initial access.
What is Pastebin? Uses, Risks, and How It Works
Pastebin is a free site for sharing plain text and code via a link. How Pastebin works, its legitimate uses, security risks, and how attackers abuse it.
What is Personally Identifiable Information (PII)?
Personally identifiable information (PII) is any data that identifies a specific person. PII types, examples, exposure risks, and the laws that govern it.

Start your demo now!

Schedule a Demo
Free 7-day trial
No Commitments
100% value guaranteed

Related Knowledge Base Articles

No items found.